AgentSpot
Trusted AI Agents, Built for the Enterprise
AgentSpot is ThoughtSpot's Multiplayer AI workforce platform: a secure, governed platform for building AI agents, workflows, and apps for enterprises.

What Is AgentSpot?
Think of AgentSpot as a team of intelligent daily assistants organized into three core areas, with every action governed and auditable.

AI Agents
Select from pre-built agents or create custom ones through a natural-language interface. Agents connect to your tools, reason over your data, and take actions on your behalf, all within a governed security boundary.

Dynamic Apps
Build and share interactive, AI-powered data experiences. Apps surface live business insights with real-time data grounding: no stale data and no code required.

Purpose-built Workflows
Schedule multi-step automations that fetch data, apply AI reasoning, and act on results automatically. Every workflow is reviewed by a human before it goes live.
AgentSpot Platform Security
AI agents that read real data, invoke real tools,
and take real-world actions require security that
goes far beyond traditional SaaS. AgentSpot's
security is not inherited from infrastructure
providers; it is designed into the application
architecture itself.
AgentSpot Secure Architecture
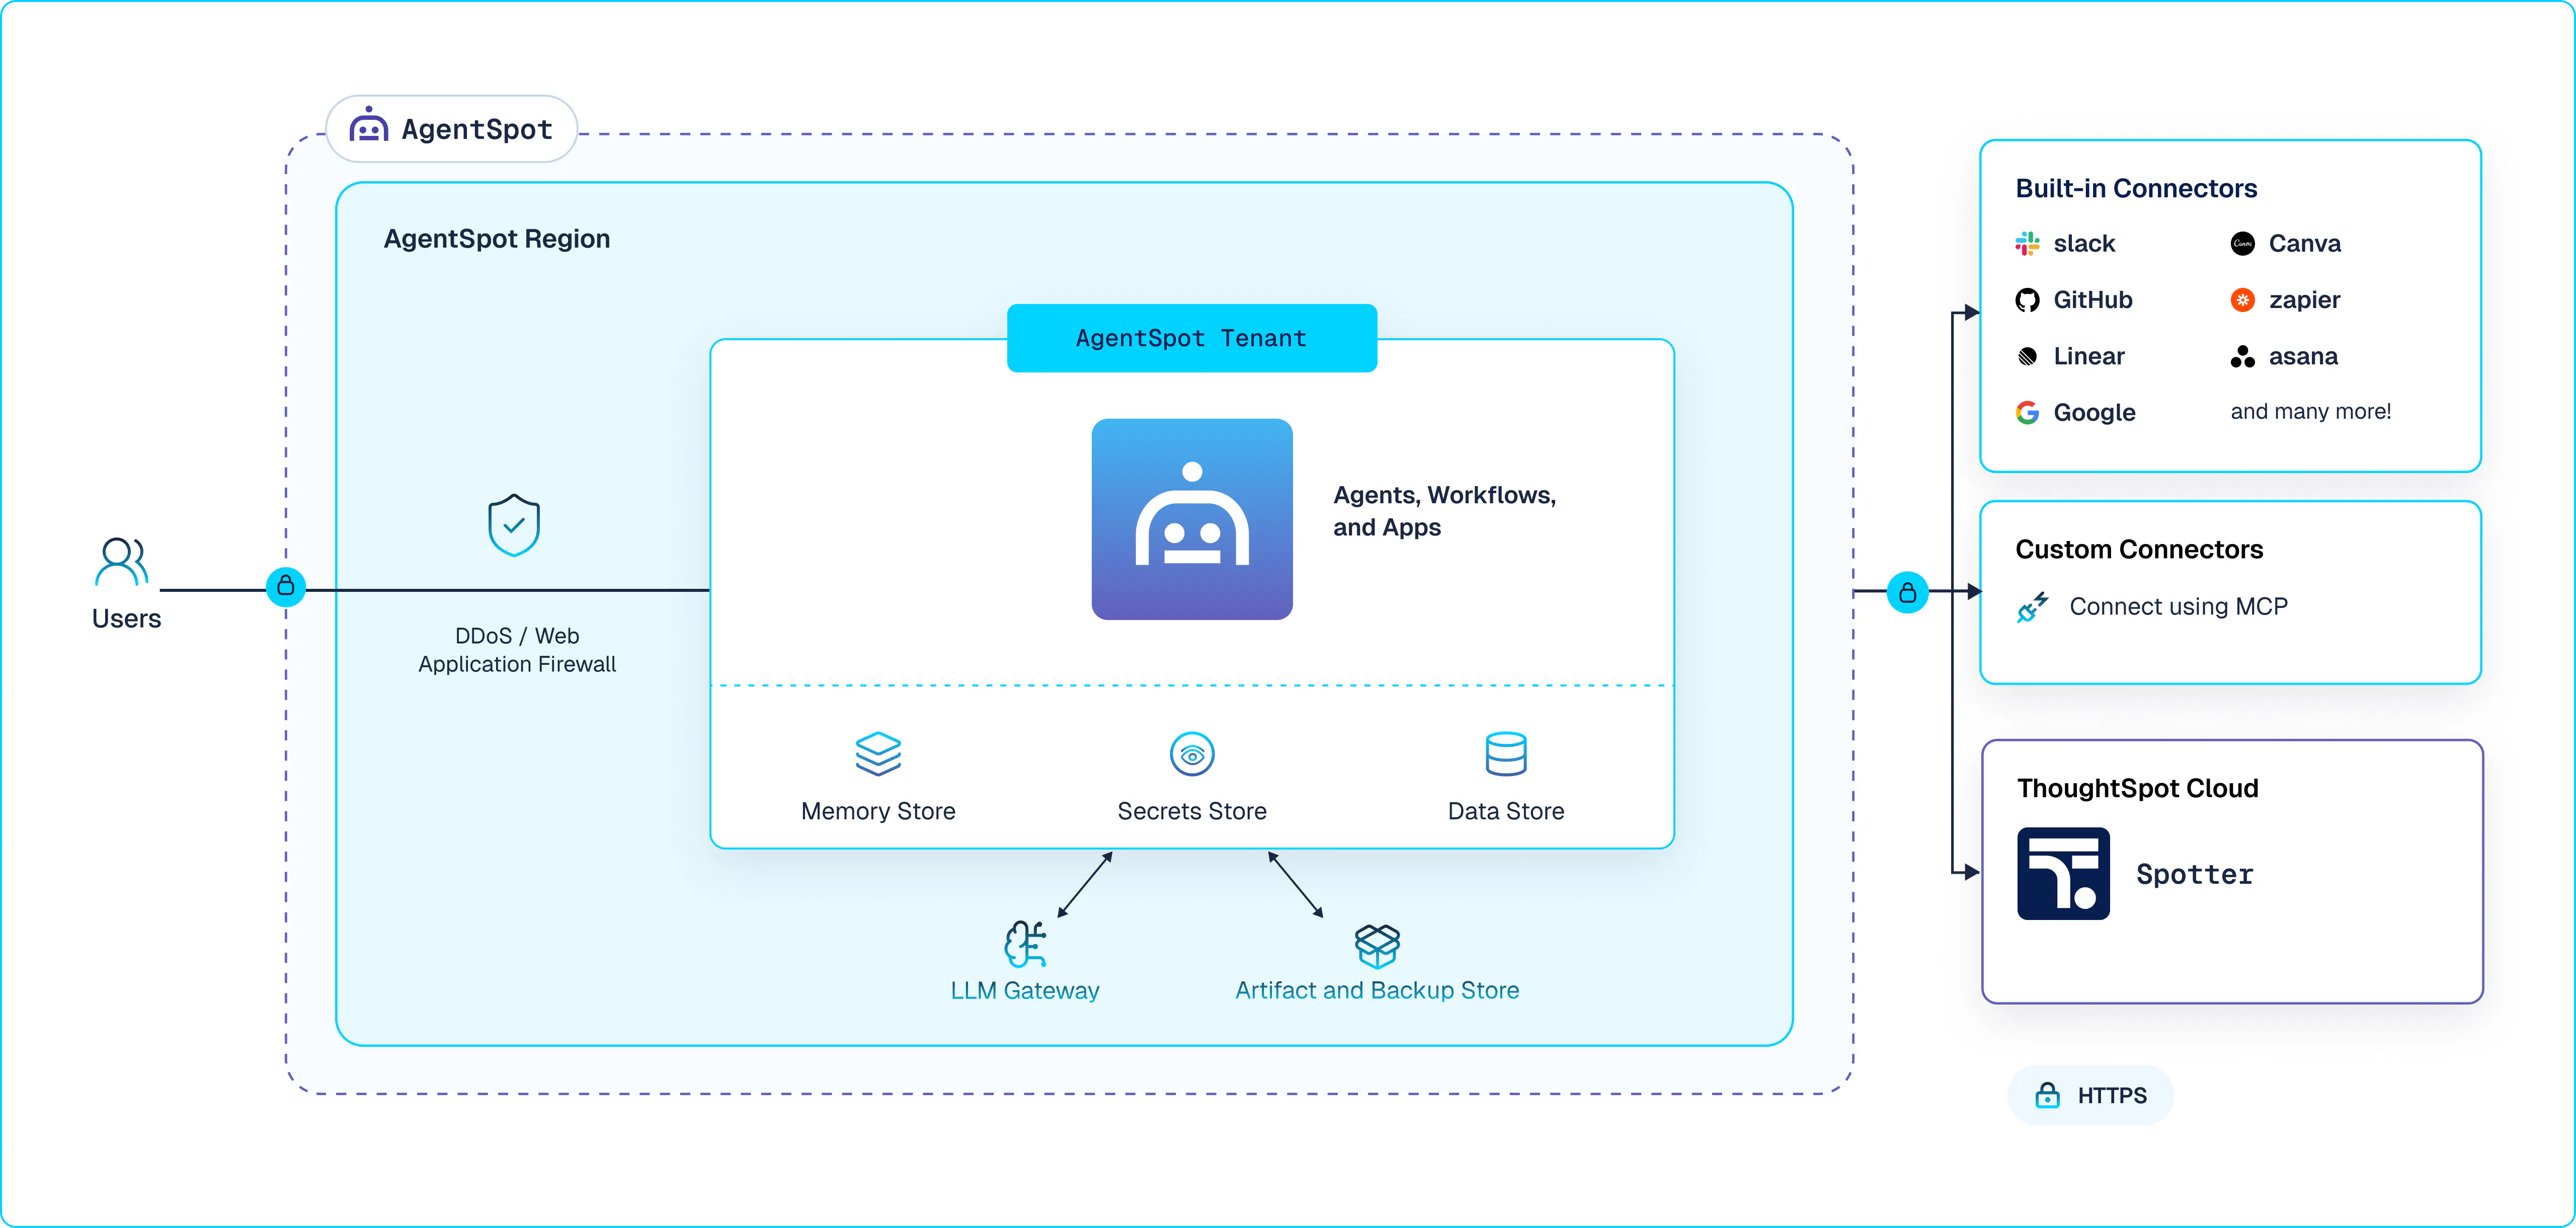
Identity and Access Controls
- AgentSpot authenticates through your organization's existing identity provider through single sign-on / SAML.
- Multiple roles allow tailored role-based access, for regular users, tenant admins, read-only access, and more.
- Every request is authenticated and checked for active tenant membership and roles using zero trust principles.
- Every session is isolated and bound to a specific tenant, with tenant filters enforced independently at both the application and database layers.
Monitoring, Logging, and Auditability
- Every AI call, tool invocation, and data mutation is logged with actor identity, timestamp, resource, and IP Address.
- Audit log entries are never deleted, and are available for self-service export by administrators.
Data Handling, Encryption, and Residency
- Execution environments are cleaned up after every run to prevent data leakage between sessions.
- Internal data is protected by row-level security independent of application logic; a mis-scoped query returns zero rows rather than someone else's data.
- All data in transit is encrypted with TLS.
- Data residency options are available in the United States and the European Union.
Secure Enterprise Agent Deployment
Building agents for enterprise use means more than giving them access to data. It means giving your organization control over what agents can do, visibility into what they've done, and confidence that they'll behave the same way tomorrow as they did today.
Human Oversight & Control
- Administrators control which AI agents are available across the organization.
- Workflow deployments and other consequential actions require explicit human confirmation before they go live.
- Any in-flight agent or workflow action can be cancelled by a user in real time.
Agent Permissions & Access Control
- Shared agents run on the executing user's own credentials (not those of the agent's creator) ensuring agents can only access what the user can. Credentials are stored per-user in a secret store, separate from the agent.
- Agents, Workflows, and Apps only ever access data the executing user is authorized to see.
- Each agent has an explicit, user-approved list of tools and cannot call tools it wasn't granted.
- Tool access is governed by a customer's administrator.
Managed Data and Connectors
- Connectors (e.g., for Slack, Jira, etc.) are managed so administrators can ensure agents work only with authorized data and systems.
- Data questions rely on your ThoughtSpot Cloud-governed data models, enforcing RLS and any other controls implemented through ThoughtSpot.
Threat Mitigation & Security Architecture
- Memory is treated as data, never as instructions. Agent memory is ranked below platform safety rules and never executed as a command, preventing memory-poisoning attacks.
- The AI model cannot call external tools directly; every tool call is intercepted, validated, and logged by a separate connector service.
Auditability & Observability
- Every model call is routed through a managed, rate-limited, fully logged gateway.
- User activity and agent use is logged for each interaction.
Responsible AI
- Your data is never used to train the underlying AI models, under agreement with model providers.
- Agents have clearly defined scopes authorized by customers, where what they can do is clearly defined.
- The data sent to an LLM model is controlled, with no data retention by the third-party providers.


Ask AI for a summary about
ThoughtSpot


Follow us


