- Start with one bounded workflow, including its user, decision, approved data, permitted actions, handoff, and success signal.
- Choose the embedding boundary based on product fit, security, engineering ownership, interface control, and long-term maintenance.
- Keep identity, authorization, tenant boundaries, and high-risk approvals outside the model.
- Pass only the context needed for the current task, then track quality, risk, latency, and user corrections after release.
Embedding agent consoles into existing systems is a product architecture decision, not a chat-window task. You need to decide where the console belongs, what it knows, what it can do, and who owns its behavior after launch.
A useful console connects trusted business context, governed definitions, user permissions, and the workflow where a decision happens. The framework below helps product leaders and technical architects make those choices before an SDK or interface pattern narrows the options.
Start With the Workflow, Not the Chat Window
A chat box gives a user somewhere to type, but it does not define a useful job. Before choosing a console layout, name the decision or task that the agent should help your user complete.
Start with one bounded workflow. Broad goals such as “help customers analyze data” leave too many product, security, and engineering questions unanswered.
A bounded workflow might help a user investigate a change in account activity, review a service issue, or prepare a status update. Each example has a recognizable trigger, a limited data scope, and a point where the user decides what happens next.
Document the workflow with a short contract:
User: Identify the person completing the task, including role, tenant, and relevant permissions.
Trigger: Record what starts the interaction, such as an alert, page visit, selected record, or user question.
Decision: State what the user needs to understand, choose, approve, or send.
Approved data: List the records, fields, definitions, and sources available for the task.
Permitted actions: Name the read and write operations available within the workflow.
Handoff: Define when the agent should stop, ask for help, or return control to an established process.
Success signal: Choose an observable outcome, such as a completed review, accepted answer, or approved action.
Next, classify the interaction. Question answering returns information, guided analysis helps the user explore a problem, task execution performs a bounded operation, and workflow orchestration coordinates steps or systems.
Those categories carry different requirements. A read-only answer can work with a narrow data contract, while task execution needs explicit action permissions, confirmation, audit records, and recovery behavior.
Where does the console sit in the user's day? If the user starts from a customer record, incident, dashboard, or approval queue, opening a blank chat session may discard valuable context.
A better entry point can carry the current object, approved business definitions, and a clear task prompt. The user still controls the conversation, but the product gives the agent a useful starting boundary.
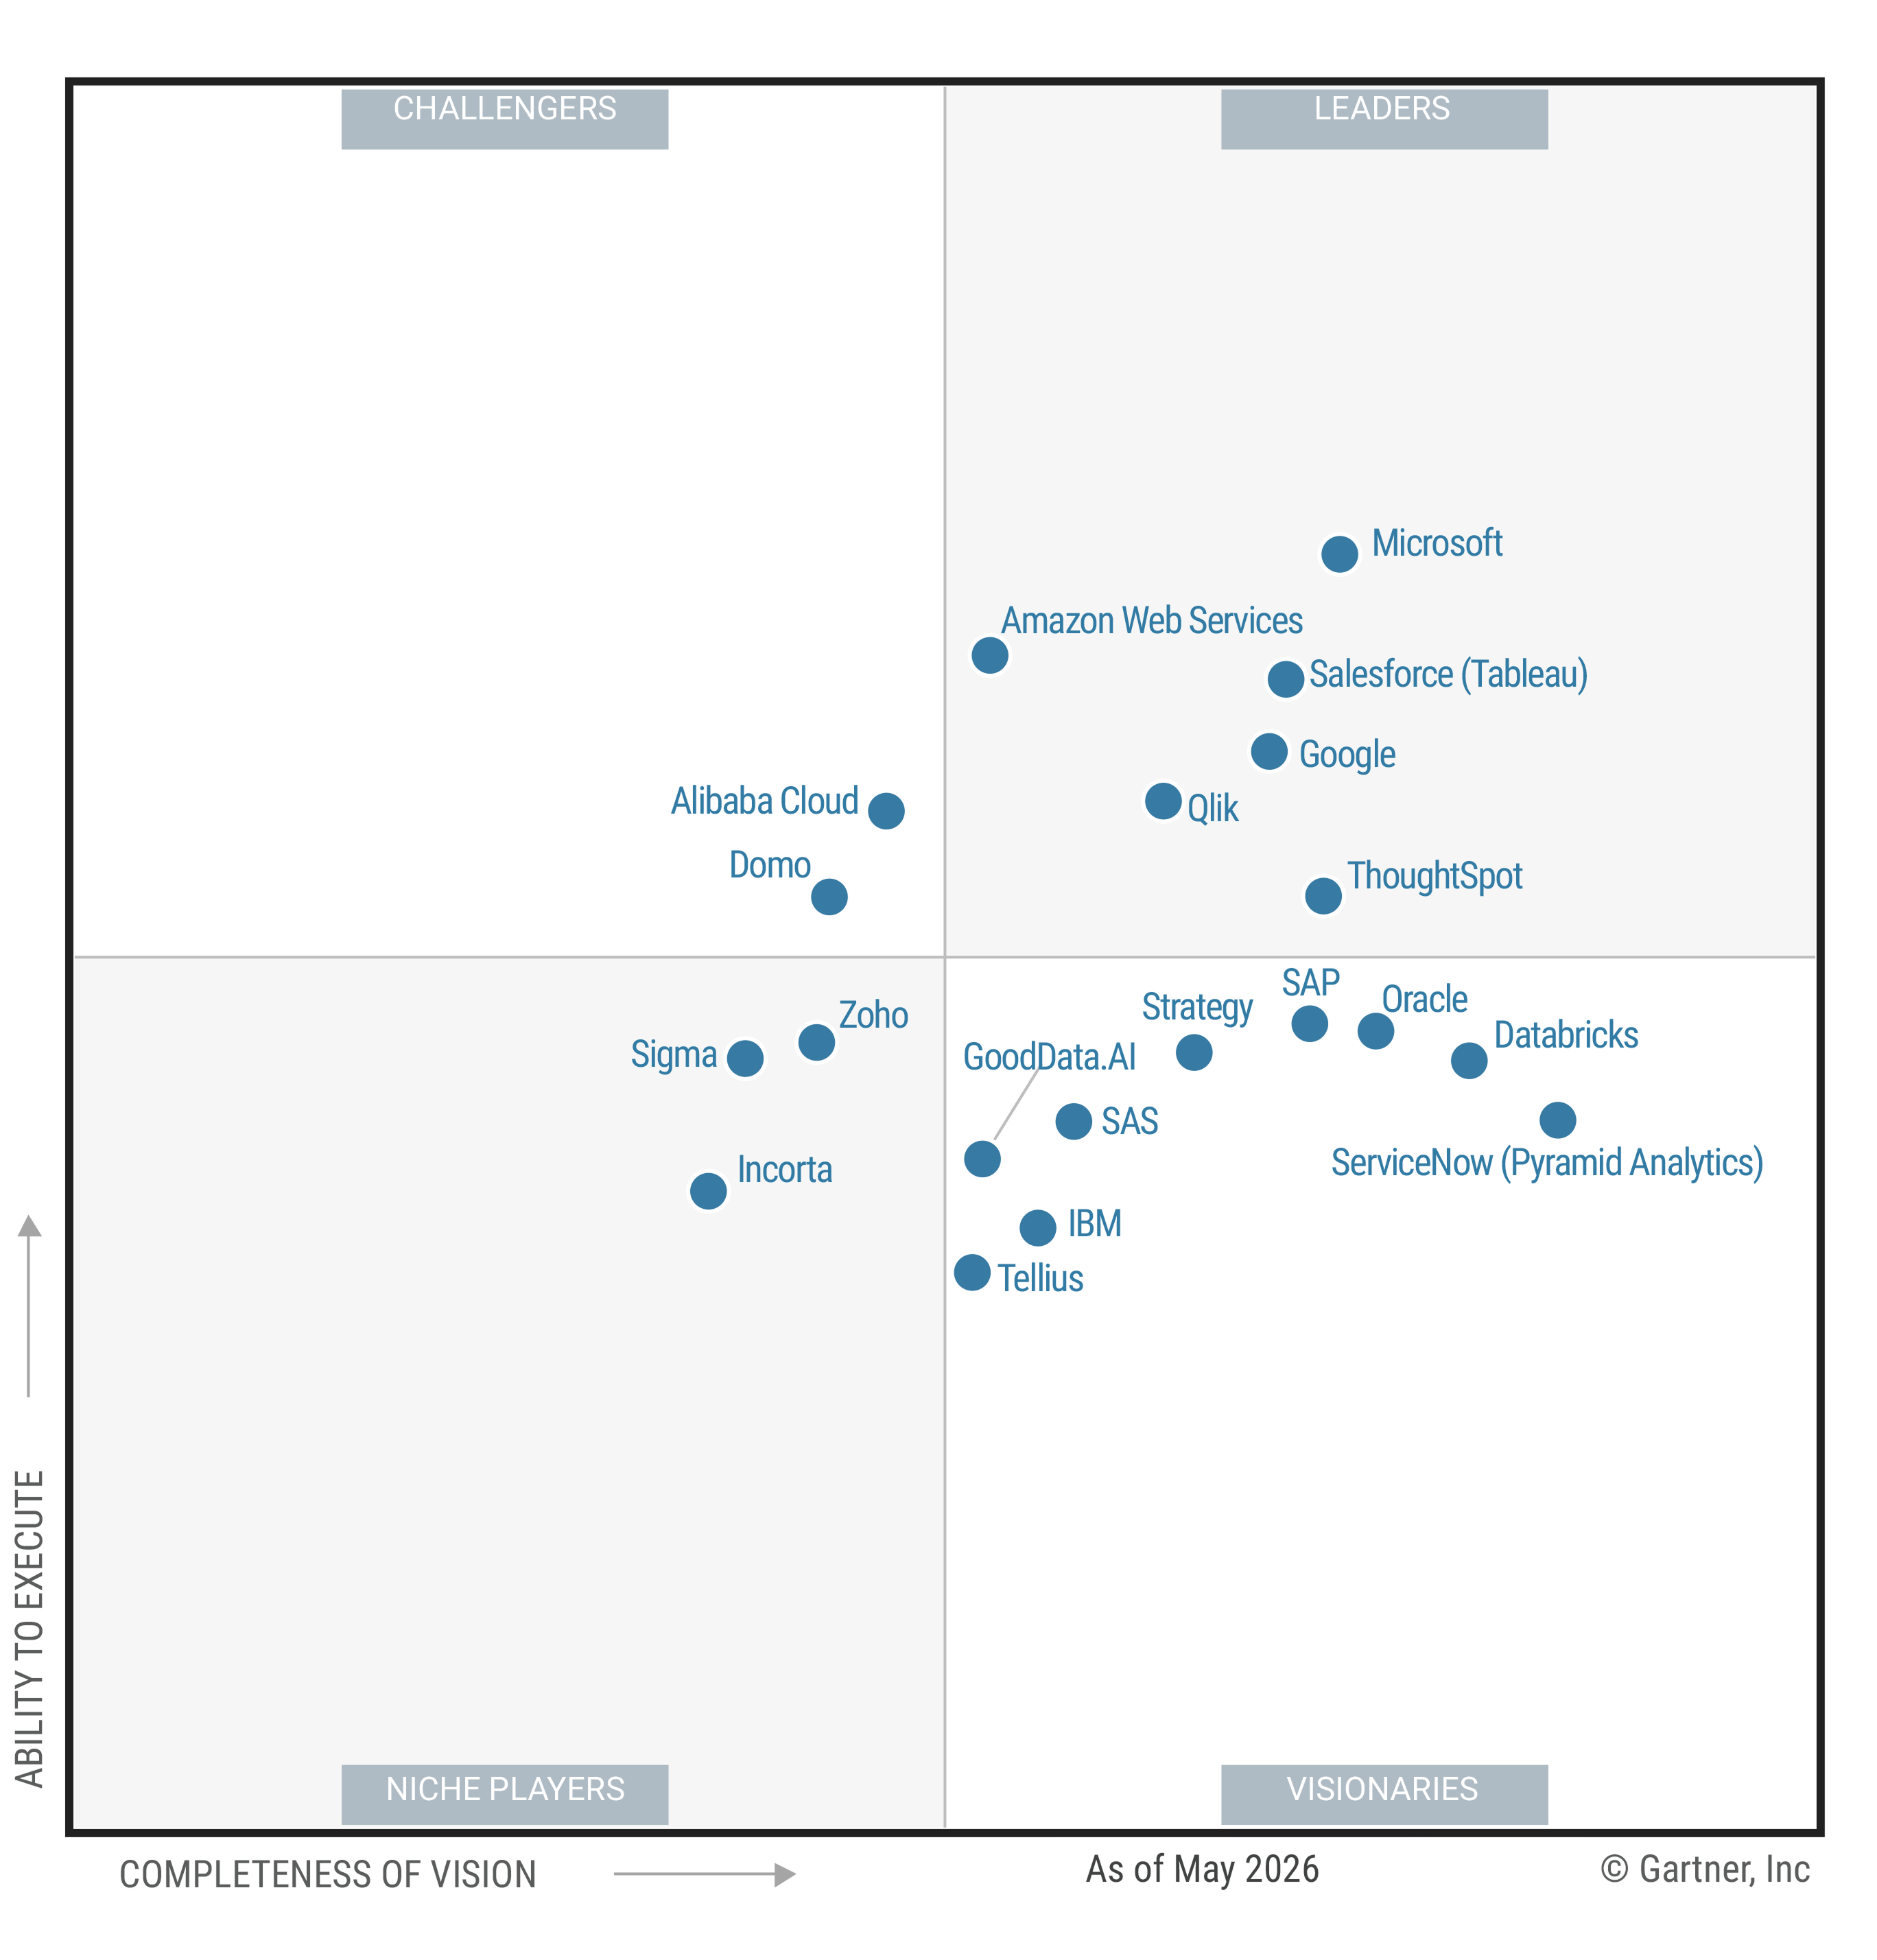
ThoughtSpot calls itself the Agentic Analytics Platform, with agent interactions grounded in business context and the workflow where a decision happens. Its approach to embedding AI agents and insights reflects a product principle: bring analysis into the business application instead of separating it from the task.
Keep the first release narrow enough to inspect. One well-defined workflow gives your team a clearer basis for interface design, security review, context testing, and measurement than a general-purpose assistant.
Choose the Right Embedding Pattern
Once the workflow is clear, choose where responsibility sits between your product and the agent service. The embedding pattern controls interface freedom, context exchange, security boundaries, observability, release coordination, and maintenance.
Four patterns cover most product decisions. The names may vary across vendors, but the underlying tradeoffs stay familiar.
| Embedding Pattern | Interface Control | Implementation Effort | Security Boundary | Context Passing | Observability Ownership | Long-Term Maintenance |
|---|---|---|---|---|---|---|
| Hosted console or redirect | Low | Low | Mostly separated from the host product | Usually limited to launch parameters and shared identity | Split between the product team and service provider | Lower interface upkeep, with less control over product changes |
| Embedded component or iframe | Moderate | Low to moderate | Clear browser and service boundary | Session, user, and page context can pass through a defined contract | Shared across host events and embedded-service records | Component updates require compatibility and interface review |
| SDK-built native console | High | Moderate | More host integration, with service calls behind the interface | Rich context can follow product state and user actions | Product team owns more client-side events and workflow records | Ongoing SDK, styling, accessibility, and release work |
| Headless API with custom interface | Very high | High | Product architecture controls the full request path | Fully custom contracts for context, tools, and history | Product team owns end-to-end instrumentation | Highest ownership across interface, orchestration, testing, and upgrades |
A hosted console works when speed and separation matter more than a native experience. It can also suit an early internal release where your team wants to test the workflow before committing to deeper interface work.
An embedded component keeps the interaction inside your product while retaining a defined service boundary. The pattern fits teams that need a branded surface and product context without owning every interaction detail.
An SDK-built console gives you more control over navigation, styling, product state, and surrounding actions. ThoughtSpot's Visual Embed SDK documents one route for integrating embedded experiences into a host product.
A headless API puts your product team in charge of the complete interface and orchestration path. Choose that route when the agent experience is a distinct product capability, the workflow needs custom controls, or your architecture requires a specific request path.
How should you choose? Begin with product differentiation: if the console is central to how customers use your product, more interface control may justify greater ownership.
Then look at engineering capacity and release cadence. A custom interface brings more tests, accessibility work, telemetry, state management, error handling, and compatibility planning into your backlog.
Security and compliance also affect the boundary. Ask where identity resolves, where permissions are checked, which system records actions, and whether the host product can review every tool request before execution.
Finally, decide who owns observability. A polished interface has limited value if your team cannot connect a user request to retrieved context, tool calls, latency, errors, approvals, and the outcome.
ThoughtSpot's embedded analytics platform supports modular components, customizable conversations with Spotter, APIs, SDKs, and developer workflows. Those options illustrate why pattern selection should follow the workflow and operating model rather than precede them.
Vendor snippets can show how to mount a component or call an endpoint. Your decision framework should first answer a harder question: which responsibilities belong inside your product for the next several release cycles?
Make Identity, Data Access, and Actions Explicit
An embedded agent inherits the trust expectations of the host product. Users will assume that the console respects their account, tenant, role, data scope, and action permissions, even when the interface feels conversational.
Treat identity, authorization, data access, and action approval as separate controls. Combining them into one model prompt makes the boundary hard to test and harder to audit.
Start with host-product identity. The server should resolve the signed-in user, tenant, role, session status, and applicable policy before any request reaches the agent workflow.
Next, calculate the user's data scope through the same governed rules that apply elsewhere in the product. Do not send a broader record set and ask the model to filter it after retrieval.
Action permissions need their own map. Reading an account summary, drafting a note, updating a record, sending a message, and triggering an external process carry different consequences.
Your permission model can assign each operation to one of four states: unavailable, read-only, allowed with confirmation, or allowed after a separate approval. That map gives product, engineering, and security reviewers a shared artifact.
OWASP's OWASP prompt injection guidance calls for authorization and least privilege outside the model, plus human approval for high-risk actions. Apply that direction at the server and tool layers, where your system can reject requests regardless of generated text.
Keep high-risk confirmation specific. A message such as “Proceed?” gives the user little basis for review, while a confirmation names the action, target, changed fields, and expected side effect.
Separate analysis from execution whenever the workflow permits it. The agent can prepare a recommendation or draft, then the host product can present a familiar control for approval.
Governed analytics follows the same principle. The Spotter AI analyst supports embedded use, governed data access, row-level security, and role-based access control.
Use a security-boundary checklist before release:
Authentication: Does the server verify the active user and session for every request?
Authorization: Does each data request and action pass a policy check outside the model?
Tenant isolation: Can any context, retrieval path, cache, or tool cross a tenant boundary?
Secrets: Are credentials kept outside prompts, browser state, transcripts, and model-visible context?
Tool permissions: Does each tool receive only the operations and resources needed for the workflow?
Audit records: Can reviewers connect the user, context, request, approval, action, and outcome?
Approval gates: Do high-risk or irreversible actions require clear human review?
Failure behavior: Does the system stop safely when identity, policy, or scope cannot be resolved?
Test the boundaries with denied cases, not only expected paths. Include expired sessions, changed roles, missing tenant data, unauthorized objects, altered tool arguments, repeated submissions, and revoked access during a conversation.
The model can explain a denial in plain language, but it should not decide whether the denial applies. Your product's policy layer remains the authority.
Pass Context Without Leaking It
Context makes an embedded console relevant, but unrestricted context creates privacy, security, and product-quality problems. A context contract defines what the product may send, what the agent may retrieve, how long information persists, and what must never cross a boundary.
Write the contract before connecting the full application state. Product and engineering teams can then review each context field against the workflow, user permission, retention policy, and expected response.
Separate context into clear categories:
Session context: Request identifiers, locale, current session state, and temporary workflow status.
User context: User ID, tenant ID, role, approved preferences, and applicable permission references.
Business definitions: Governed metric definitions, entity relationships, calculation rules, and approved terminology.
Page or object context: The selected account, incident, dashboard, order, or record relevant to the current task.
Conversation history: Prior turns retained for the active workflow under an explicit history policy.
Retrieved data: Records returned after authorization and filtered for the current request.
Send identifiers and governed definitions when the agent can retrieve approved records through a controlled path. Dumping a page's full state into a prompt can expose hidden fields, unrelated records, implementation details, and stale values.
Use the minimum context needed for the task. Minimum does not mean vague; it means every field has a stated purpose, permission basis, source, and lifetime.
Freshness matters in operational workflows. Record when context was read, which source supplied it, and whether the agent should refresh before answering or proposing an action.
Provenance helps the interface explain what shaped the response. The user may need to know which account, time period, governed definition, or selected object the agent used, without seeing internal prompt instructions.
Redaction should happen before model-visible context is assembled. Masking text after generation cannot prevent the model from processing information that should never have entered the request.
Retention needs a separate choice for each context type. A page selection may last one turn, workflow state may last one session, and approved conversation history may follow a defined product policy.
Plan for missing and conflicting context as well. When the selected record is unavailable or two definitions disagree, the console should ask a focused question, show the conflict, or stop the affected action.
For conversational analytics, the ConversationEmbed API offers a documented interface for embedding a conversation experience. The surrounding product still needs a clear contract for identity, selected context, approved data, and user-visible state.
Trusted business context gives an analytics agent more than raw fields. Governed definitions connect the user's language to the metrics, entities, and relationships that matter inside the workflow.
That grounding supports ThoughtSpot's position as the Agentic Analytics Platform. The useful product question is not how much context you can send, but which governed context the user needs for the current decision.
Design the Console as Part of Your Product
Your agent console should feel connected to the product without hiding its boundaries. Treat it as a product surface with the same information architecture, interaction standards, accessibility expectations, and support paths as surrounding features.
Begin with the entry point. A side panel can support quick questions beside a record, while a full-page workspace fits longer analysis with sources, history, and multiple steps.
A modal works for a brief, interruptive task that must finish before the user returns. Inline interaction suits a focused action or explanation tied to one field, chart, alert, or object.
Give users scope cues before they type. The interface can name the selected object, available data range, permitted actions, or current workflow so the user knows what the console can address.
Suggested prompts should represent real tasks, not broad demonstrations. “Summarize changes for this account” gives more direction than “Ask anything,” particularly when the product has already supplied account context.
Show meaningful system state during retrieval and tool use. Loading text can identify whether the console is checking data, preparing a response, or waiting for approval without exposing internal reasoning.
Error states need an action. Tell the user whether to retry, adjust the request, refresh access, remove an unavailable action, or return to an established workflow.
When the agent proposes a write action, present the change in product language. Include the target, affected fields, destination, and confirmation step before execution.
Fallbacks belong in the design from the start. A user may need to open the underlying record, contact support, hand off to a specialist, or continue through a manual process.
Visual customization should preserve system boundaries. Match typography, spacing, color, and component behavior, but keep permissions, sources, confirmations, and agent status easy to recognize.
Accessibility applies to the complete flow, including launch controls, conversation history, generated content, loading updates, errors, and confirmations. W3C's WCAG 2.2 states that user-interface components and navigation must be operable, and keyboard-operable UI needs a mode with visible focus.
Use an interface review checklist:
Can a keyboard user open, navigate, submit, review, confirm, cancel, and close the console?
Does visible focus remain clear as new content, actions, and errors appear?
Are loading updates and status changes available without relying only on visual motion?
Can users identify the active object, data scope, and available actions?
Do confirmations describe the exact action and target?
Can users recover from a timeout, denied request, missing record, or tool error?
Does the console offer a clear route back to the host workflow?
The console should also respect established navigation. Preserve browser behavior, deep links, back-button expectations, and unsaved product state when users open or close the experience.
Finally, test with the people who own the surrounding workflow. Product usability feedback matters, but security, support, accessibility, and operations teams will spot different failure paths.
Roll Out, Measure, and Improve the Experience
A staged rollout gives your team room to inspect behavior before broad availability. Start with internal users who understand the workflow, then move to a bounded customer cohort with known permissions, data, and support contacts.
Set release gates around observable behavior. Your team should know what quality, safety, latency, and task-completion signals will pause expansion or trigger rollback.
Assign ownership across the operating model:
Product: Workflow scope, user value, interface behavior, release decisions, and success measures.
Engineering: Integration boundaries, reliability, telemetry, state management, and rollback.
Data: Governed definitions, source quality, retrieval behavior, and context freshness.
Security: Identity, authorization, tenant boundaries, tool permissions, and incident review.
Support: User-reported failures, escalation routes, known limitations, and recovery guidance.
Legal and privacy: Approved data use, retention, disclosure, and regional obligations that apply to the product.
Measure whether the console helps users finish the intended task. Task completion and answer acceptance give a stronger product signal than message volume alone.
Track fallback rate, tool errors, latency, user corrections, escalation, unsafe action attempts, and repeat use. Review those measures by workflow, tenant type, role, release version, and embedding pattern where appropriate.
Quantitative signals need conversation review and support feedback. A completed interaction may still contain confusing wording, a poor source choice, an unnecessary refusal, or a workaround that the metric misses.
Create a review sample that includes successful tasks, abandoned sessions, denied actions, corrected answers, high latency, and escalations. Remove or restrict sensitive content before reviewers receive transcripts.
NIST's NIST AI RMF Playbook organizes AI risk work around Govern, Map, Measure, and Manage. That structure can support a recurring product review rather than a one-time launch check.
Govern names owners, policies, decision rights, and escalation paths. Map connects the workflow to users, context sources, actions, affected parties, and potential harm.
Measure covers product quality, security behavior, reliability, accessibility, and user outcomes. Manage turns those findings into release decisions, mitigations, incident response, and follow-up work.
Keep an observability and release checklist for every material change:
Prompt or instruction revisions
New context fields or retrieval sources
Added tools, write actions, or permission scopes
Model, service, or vendor changes
Interface and confirmation updates
Identity, tenant, or policy changes
New metrics, alerts, and review samples
Incident playbooks and rollback steps
Version those changes so a reviewer can connect behavior to a release. When an incident occurs, the team should identify the active instructions, context contract, tools, permissions, and interface version.
Improvement should stay tied to the bounded workflow. If users repeatedly ask for a different task, treat that demand as a product decision rather than quietly broadening the agent's scope.
Build a Console That Fits the Workflow and Holds Up in Production
A production agent console depends on six connected decisions: workflow scope, embedding pattern, access controls, context contract, product design, and operating ownership. Weakness in one area will shape the user's experience across the rest.
The right boundary depends on your product, users, risk, and engineering ownership. A hosted experience may fit an early bounded release, while a native SDK or headless interface may suit a differentiated product capability.
Before selecting a component or starting interface work, document one workflow. Write down its identity, data, context, action, confirmation, measurement, and rollback contracts, then ask each owner to review the same artifact.
If you want to explore governed conversational analytics inside a product, start a ThoughtSpot free trial. Keep the first implementation focused on a real user decision, then expand only when the operating evidence supports another workflow.